Hi,
Is anyone else seeing a similar issue to this?
I have a custom container both on my main site and wordpress blog.
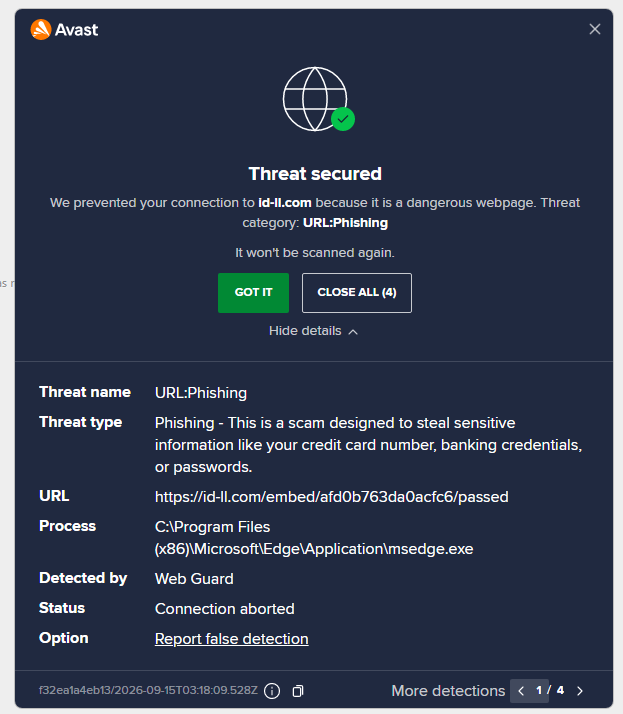
I’ve noticed Avast is blocking my blog because of a phishing detection for id-il.com.
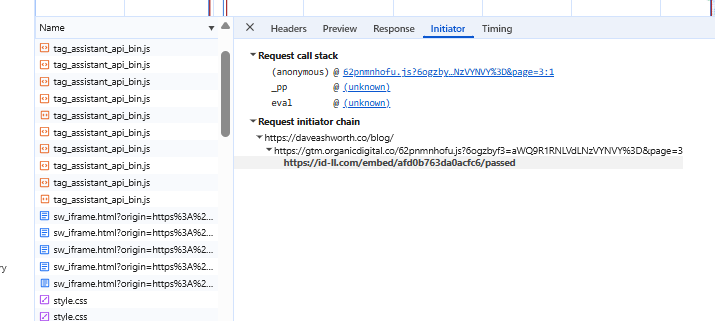
I’ve traced the request in Chrome DevTools and the initiator chain shows it coming from my Stape custom GTM loader at gtm.organicdigital.co/62pnmnhofu.js.
The chain shown in DevTools is:
Dave Ashworth's Blog - → gtm.organicdigital.co/62pnmnhofu.js → id-il.com/embed/.../passed
Avast identifies id-il.com as URL:Phishing and blocks the request, which is preventing the page from loading correctly.
Anyone know why the Stape loader is making a request to id-il.com, and whether this is expected behaviour?
It currently appears to happen only under /blog/, which is WordPress.
But the same custom loader is used across the rest of the site without triggering the request.